When a celebrity account is hacked, the takeover almost always starts with a person, not a mystery. Someone gets a password or a login session, locks the real owner out, and posts under a name millions of people trust. The account is not gone. The platform can restore it once the owner proves identity, and that restoration follows a fairly predictable path.
The hard part for readers is the first hour. A strange post from a famous account looks identical whether it is a hack, a prank by the celebrity, or a fake account imitating one. The difference is in the details, and those details are checkable.
This explainer covers how takeovers actually happen, what platforms do to hand accounts back, and the quick checks that separate a real compromise from noise. For the related problem of accounts that were never real in the first place, see our guide to Fake celebrity accounts: how to spot an impersonator in 60 seconds.
How does someone actually take over a famous account?
Most takeovers use one of a handful of well-known doors, not exotic techniques. The most common is credential reuse: a password that appeared in some older breach of an unrelated service, tried against the celebrity's email or social login. If the star reused that password and had not turned on extra verification, the attacker walks in.
The second door is phishing. Someone sends a convincing message that looks like a platform warning or a brand-deal inquiry, and the recipient signs in through a fake page. The attacker captures the login and the session, then changes the recovery email and phone number so the real owner cannot reset.
A third door is the insider or contractor path. Publicists, managers, social media managers, and agencies often hold posting access. A departing employee, a stolen laptop, or a compromised agency account can expose credentials without the celebrity ever being phished directly. Phone-based takeovers, where an attacker tricks a mobile carrier into moving a phone number to a new SIM, are rarer but have historically hit high-profile targets because the number often guards the reset process.
What you rarely see in a genuine takeover is a technically dramatic breach of the platform itself. The big services are hard targets. The celebrity's own habits are usually the soft spot.
What does the platform do to give the account back?
Restoration is an identity process, and it is deliberately slow. The real owner typically contacts the platform through an official help channel and proves control through government identification, prior email addresses, device history, or other account details only the legitimate holder would know. Platforms do not restore access based on a public tweet saying "I was hacked," because that tweet could come from anyone.
While the review runs, the platform usually freezes the account or strips its verification badge. That freeze matters for readers: a verified badge that suddenly disappears from a famous account during a strange episode is a meaningful signal, though it is not proof on its own.
Once identity is confirmed, the platform removes the attacker's recovery details, forces a password reset, and invalidates active login sessions so stolen sessions stop working. The offensive posts sometimes stay up until the owner regains access and deletes them, which is why screenshots of the fake posts circulate long after control is restored. The honest record of an incident therefore has two timestamps: when the takeover happened and when the account came back.
How can you tell a hack from a prank post?
Start with the three registers this site uses for any viral claim: confirmed, unconfirmed, or false. A post is confirmed as a hack only when the celebrity or their team says so on the record, or the platform confirms a compromise. It is unconfirmed when the post is odd but nobody with standing has spoken. It is false when the account was never the real one in the first place.
Several checks help you place a strange post in one of those buckets:
- Check the handle character by character. Extra underscores, swapped letters, and added numbers are the classic impersonator tells. Many "hacks" that go viral are actually brand-new accounts with near-identical names.
- Look at the account age. An account created last week claiming to be a twenty-year star is an impersonation, not a takeover.
- Watch for the follow-up. Real takeovers are usually followed by a statement from the star's team through another verified channel, a publicist, or a mainstream outlet. Silence for days points toward either a prank the star is enjoying or a fake account.
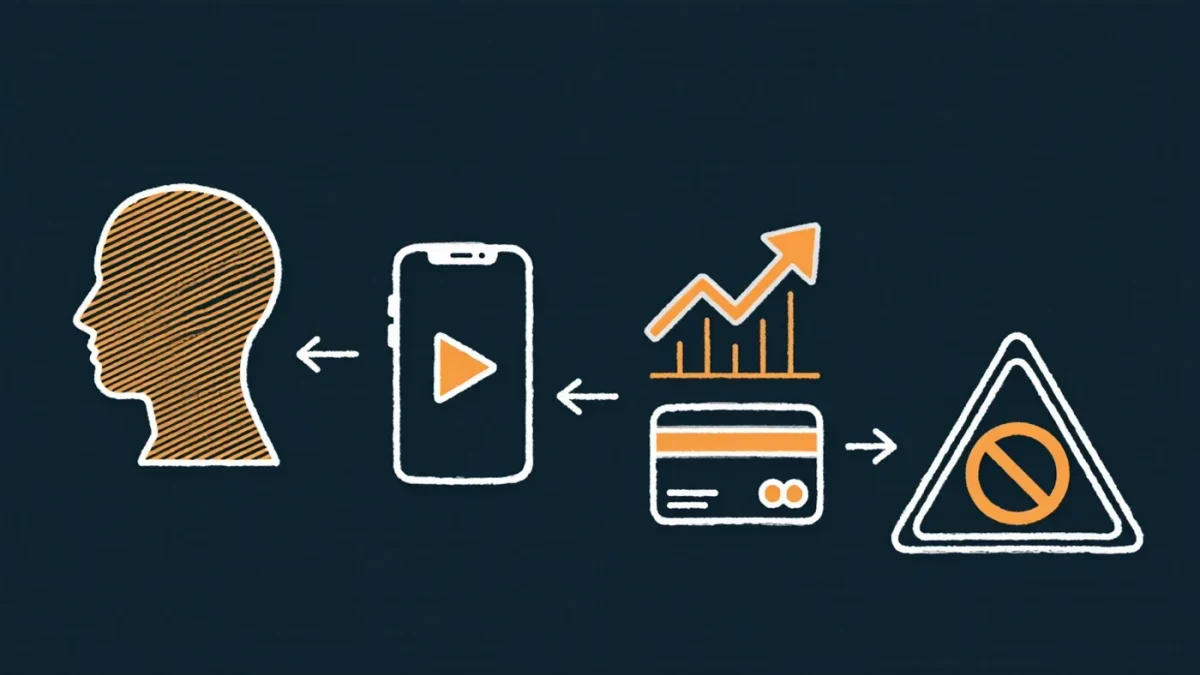
- Notice the ask. Posts pushing a crypto giveaway, a limited investment, or an urgent link are the standard payload of account takeovers and fake-celebrity scams alike. We broke down that pattern in AI ads using fake celebrities: how the scam actually works.
- Consider the content. A post wildly out of character can be a hack, but it can also be a planned stunt. Without a named statement, the honest label is unconfirmed.
One more distinction: a hacked account is a real account posting under false control. An impersonator account is a fake account from day one. Readers conflate the two constantly, and the confusion is exactly what scammers rely on.
Why do these takeovers spread so fast?
The mechanism is simple. A famous handle carries built-in trust, so anything it posts gets treated as news before anyone checks. Screenshots then travel independently of the original post, which means the fake content keeps circulating even after the account is restored and the posts are deleted. By the time the correction lands, the screenshot has been reposted thousands of times with no context attached.
This is the same lifecycle that powers other recurring celebrity falsehoods. The celebrity death hoax playbook: why it keeps working follows an identical arc: a shocking claim, rapid screenshot spread, slow correction, permanent residue. The speed asymmetry is the whole story. False posts are instant; verification takes hours at best.
What this means for readers
Our analysis of the pattern comes down to a short checklist. When a famous account posts something shocking, do not share it first. Check the exact handle. Check whether the account is old. Wait for a named statement from the star, their team, or the platform. If none arrives, treat the post as unconfirmed and say so if you repost it at all.
If you were scammed through a compromised or fake celebrity account, report the post to the platform and keep your records. Money sent to a fraudster is rarely recoverable, which is why the reporting step, not the refund hope, is the practical one.
For the celebrities and their teams, the durable lessons are equally unglamorous: unique passwords, app-based or hardware-based two-factor authentication rather than text messages, tight control over who holds posting access, and an off-platform way to reach the platform when things go wrong. None of it is new. The accounts that get taken are almost always the ones missing one of those basics.
What the evidence consistently shows is that takeovers end the same way they began: with identity. The attacker proves nothing to get in and everything is undone when the real owner proves who they are. Between those two moments, the reader's only reliable tool is patience and a second source. Treat every shocking celebrity post as a question, not a fact, until someone with a name and a channel confirms it.
Sources: celebritycruises.com · yahoo.com